Daily · Article 01 · 4 min read
- Security
- Open source
Drupal warns of a critical update. Check who will apply it
Advance notice posted 17 November JST · release window on 18 November UTC
Summary
Drupal’s security team has announced a forthcoming security update for supported branches. Check which version your site runs and who can update it.
Key facts
Drupal is open-source software for building websites and managing their content. Its security team posted an advance notice at 07:47 on 17 November JST for a critical update to Drupal’s core software. The release is scheduled for 17:00–21:00 UTC on 18 November, or 02:00–06:00 JST on 19 November. The team says at least one flaw can be exploited without signing in, and more than one site configuration is affected. The fixed version numbers for this release and any actual exploitation have yet to be confirmed. Drupal advance notice
1. The public page and the software running it
Imagine a library website with a public events calendar and an editor that staff use to change it. Drupal core is the shared software that builds the pages and decides which actions visitors and staff are allowed to take. When a flaw can be exploited without signing in, the operator has to consider exposure beyond the people who hold staff accounts. The library is a fictional example. The exact component and actions involved in this advisory have yet to be disclosed. Drupal advance notice
The cat asks Q&A
 The researcher
Would hiding the login button from visitors protect the site?
Pocket NotebookHiding a button can leave the software handling requests in the same way. Check your site’s version and configuration against the conditions in the forthcoming advisory.
2. The notice, the download and the live site
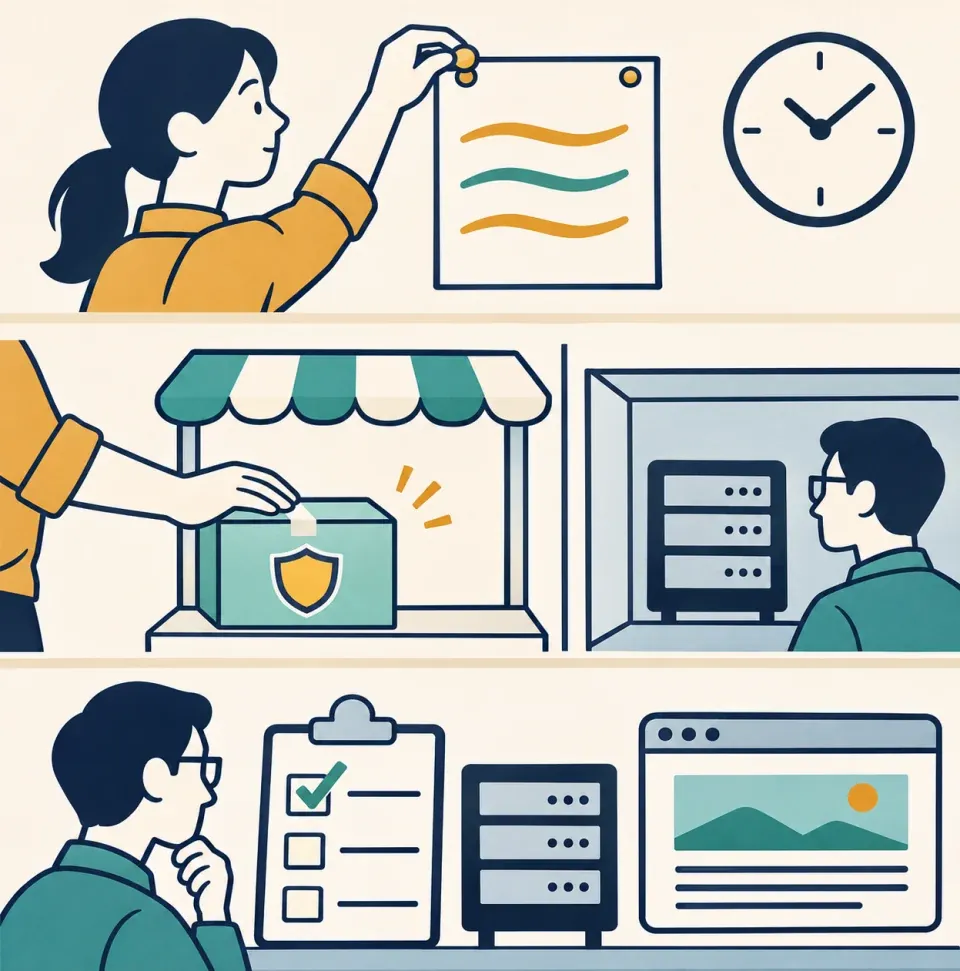
A security team can give operators time to arrange staff and make backups by announcing a release window early. After the project publishes the fix for supported branches, the site’s operator or hosting provider can install it. In our library example, downloading the fix and running it on a test copy still leaves the live site to update.
| Stage and owner | Status for this update | Evidence to look for |
|---|---|---|
| Advance notice · Drupal Security Team | Public | Scope and planned time |
| Release · Drupal project | Scheduled for 18 November, 17:00–21:00 UTC, or 19 November, 02:00–06:00 JST | Fixed versions in the advisories and release list |
| Application · site operator or host | Verify for each live site | Live version, time applied and deployment record |
- Stage and owner
Advance notice · Drupal Security Team
- Status for this update
- Public
- Evidence to look for
- Scope and planned time
- Stage and owner
Release · Drupal project
- Status for this update
- Scheduled for 18 November, 17:00–21:00 UTC, or 19 November, 02:00–06:00 JST
- Evidence to look for
- Fixed versions in the advisories and release list
- Stage and owner
Application · site operator or host
- Status for this update
- Verify for each live site
- Evidence to look for
- Live version, time applied and deployment record
The cat asks Q&A
- The researcher
If I get a release alert, does it mean our website is fixed?
Pocket NotebookThe alert tells you the fix is available. Ask the person who runs the public site for its running version and the time the fix was applied.
3. Which branch your site runs
In 11.4.x, the x stands for the patch number after 11.4. The team named the three supported branches as affected. It recommends getting onto the latest existing supported patch for your branch before the window, while there is time to deal with other upgrade problems. Use the new advisory to find the version that fixes this particular issue. Drupal advance notice · Support schedule
| Branch in use | Status in the notice | What to check |
|---|---|---|
| 11.4.x, 11.3.x, 10.6.x | Supported and in the affected scope | Latest existing patch for the branch and the forthcoming security version |
| 12.0.0-beta3, 11.5.0-beta1 | These two test versions are also in scope | Announcement of the next beta or release candidate after the supported branches |
| Older branches beyond support | Outside the current support list | Interim mitigation in the forthcoming advisory and a move to a supported version |
- Branch in use
11.4.x, 11.3.x, 10.6.x
- Status in the notice
- Supported and in the affected scope
- What to check
- Latest existing patch for the branch and the forthcoming security version
- Branch in use
12.0.0-beta3, 11.5.0-beta1
- Status in the notice
- These two test versions are also in scope
- What to check
- Announcement of the next beta or release candidate after the supported branches
- Branch in use
Older branches beyond support
- Status in the notice
- Outside the current support list
- What to check
- Interim mitigation in the forthcoming advisory and a move to a supported version
The cat asks Q&A
- The researcher
If I update to the current latest patch today, is the scheduled security work done?
Pocket NotebookToday’s existing patch is preparation. Once the advisory is out, check that the public site is running the fixed version for its branch.
4. Running the site yourself or relying on a host
Drupal Steward filters certain requests before they reach a website. The security team says it mitigates the known attack vectors for this issue. Another advisory on the same day may fall outside that protection. Drupal’s update guide calls for a backup and testing the update in a development environment for a live site. Drupal advance notice · Drupal Steward · Update guide
| Who runs the site | Before release | After release |
|---|---|---|
| Your own team | Check current version, backup and test environment | Apply the official update and check the live version and important pages |
| Hosting provider | Confirm who updates core and when they will report back | Ask for the version, time applied and result of the live-site check |
- Who runs the site
Your own team
- Before release
- Check current version, backup and test environment
- After release
- Apply the official update and check the live version and important pages
- Who runs the site
Hosting provider
- Before release
- Confirm who updates core and when they will report back
- After release
- Ask for the version, time applied and result of the live-site check
The cat asks Q&A
- The researcher
What evidence should I ask a hosting provider to send?
Pocket NotebookAsk which live site they updated, to which version, and when. You can also ask whether they checked that important pages or editor functions still work.
To close
Assign someone to check each live site
Before the release window, record each site’s current version and who handles the update. When the fix is out, use the advisory to match each branch to its fixed release and write down when the live site was verified.
Sources
- Drupal advance notice PSA-2026-11-16drupal.org
- Drupal security advisoriesdrupal.org
- Drupal core releasesdrupal.org
- Drupal core support and release scheduledrupal.org
- Drupal Stewardnew.drupal.org
- Drupal core update guidedrupal.org